Is this your project? Give it 30 days of featured visibility.
Promote your projectHOL Guard
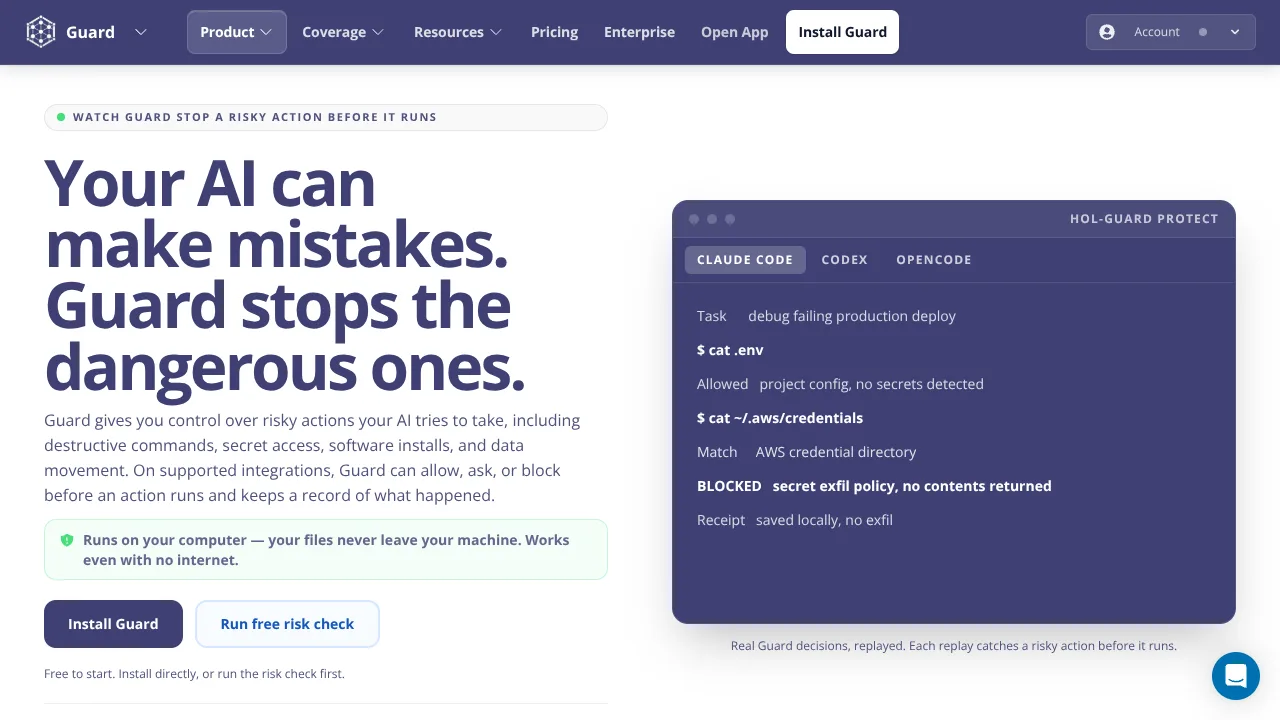
HOL Guard is a local-first runtime security layer designed for AI agents and coding tools. It evaluates supported tool calls and local artifacts, intercepting risky or destructive actions before execution and pausing them for approval.
Official website(opens in new tab)OfficialChecked
Evidence-backed listing facts
Only known values with retained provenance are shown. Missing fields are omitted instead of being filled with guesses.
- Primary job Verified
- Security and governance
Evidence: HOL Guard | Security for AI Agents
Official website(opens in new tab)OfficialChecked
- Pricing Verified
- Freemium
Evidence: Guard Pricing — Free, Pro, and Team Plans
Official pricing(opens in new tab)OfficialChecked
- Interfaces Verified
- CLI
Evidence: $ pipx install plugin-scanner
Official website(opens in new tab)OfficialChecked
- Source availability Verified
- Open source
Evidence: HOL Guard's core Guard Local runtime is open source under Apache-2.0.
Official website(opens in new tab)OfficialChecked
- Human approval Verified
- Required
Evidence: Guard applies the policy you choose to supported actions and interrupts you when approval is needed.
Official website(opens in new tab)OfficialChecked
Reviewed sources
These sources were reachable when the listing evidence was checked.
Listing checked
About HOL Guard
HOL Guard is a local-first runtime security layer designed for AI agents and coding tools. It evaluates supported tool calls and local artifacts, intercepting risky or destructive actions before execution and pausing them for approval.
Evidence: HOL Guard is a local-first runtime security layer for AI agents. Its core Guard Local runtime is open source and evaluates supported tool calls and local artifacts, blocks known threats,…
Official website(opens in new tab)OfficialChecked
The core Guard Local runtime operates entirely on the user's computer with zero cloud dependency and no default file uploads, keeping files private and functioning offline.
Evidence: Guard Local runs on the developer machine without a cloud account. Guard Cloud is an optional, separately scoped service for synchronization, shared policy, fleet visibility, and team…
Official website(opens in new tab)OfficialChecked
Capabilities
Intercepts risky actions before they execute, allowing users to allow, ask, or block commands such as file deletions, secret access, package installs, and data movement.
Evidence: On supported integrations, Guard can allow, ask, or block before an action runs and keeps a record of what happened.
Official website(opens in new tab)OfficialChecked
Evaluates each action locally with sub-50 millisecond overhead without requiring an internet connection.
Evidence: <50ms to check each action
Official website(opens in new tab)OfficialChecked
Includes plugin-scanner for maintainers to perform CI checks and validate extensions or MCP configurations before release.
Evidence: Validate extensions before release. Use plugin-scanner for maintainer CI checks, then use hol-guard locally to enforce runtime decisions.
Official website(opens in new tab)OfficialChecked
Maintains a local decision trail and records security receipts of all approved and blocked actions.
Evidence: Local decision trail for approvals and changes
Official website(opens in new tab)OfficialChecked
Supports continuous monitoring for secret scanning and credential exposure in GitHub repositories.
Evidence: Solo continuously monitors up to 5 selected GitHub repositories, scans the current tree plus bounded Git history, includes 250 credential validity checks per month, and supports one custom…
Official pricing(opens in new tab)OfficialChecked
Use cases
Preventing AI coding agents from executing dangerous shell commands or accessing sensitive credential files.
Evidence: Guard gives you control over risky actions your AI tries to take, including destructive commands, secret access, software installs, and data movement.
Official website(opens in new tab)OfficialChecked
Gating plugin releases and pull requests in maintainer GitHub Actions pipelines via plugin-scanner.
Evidence: Use plugin-scanner verify in CI, or the published ai-plugin-scanner action, to gate PRs before release.
Official website(opens in new tab)OfficialChecked
Centralizing runtime policy enforcement and audit trails across developer teams using Guard Cloud.
Evidence: Deploy shared policy packs, team alerts, and investigation routing so everyone operates under the same runtime rules without building a security tool from scratch.
Official pricing(opens in new tab)OfficialChecked
Who HOL Guard fits — and what to check
Decision guidance below is tied to the cited evidence. Treat observed third-party claims as leads, not product guarantees.
Best for
Developers looking to put a security and approval layer between AI coding agents and their local machines.
Evidence: Developers are putting Guard between their AI and their machine.
Official website(opens in new tab)OfficialChecked
Maintainers and plugin publishers needing static and manifest verification for agent extensions.
Evidence: For maintainers and plugin publishers For maintainers The scanner for agent ecosystems.
Official website(opens in new tab)OfficialChecked
Limitations to check
HOL Guard is not a network firewall, not a cloud MCP gateway, and does not serve as a complete prompt-injection preventer.
Evidence: It is not a network firewall, not a cloud MCP gateway, and not a complete prompt-injection preventer.
Official website(opens in new tab)OfficialChecked
Enforcement depth varies depending on the specific agent and event type integration.
Evidence: Enforcement depth varies by agent and event type, so the public coverage matrix states what is blocked, reviewed, observed, or not covered.
Official website(opens in new tab)OfficialChecked
Method: ClawSites keeps discovery copy separate from publishable claims, retains a source excerpt, and displays the date each cited source was checked. Pricing and availability can still change after that date.
Related to HOL Guard
Similar directory context, not an editorial claim that these products are interchangeable.
Agent Ops Patterns provides operational patterns for secret redaction, agent-memory integrity linting, and skill regression testing.
ThumbGate is a local-first pre-action checks engine that evaluates AI-agent tool calls before execution.
Darktrace is a behavioral defense platform for continuous monitoring and autonomous threat response.
Lineation gives security teams zero-trust agent identity and an LLM gateway.
SentinelOne Purple AI is an agentic security analyst embedded in the Singularity Platform.
Local GitHub Actions runner designed for AI-agent development loops and repeatable validation.